The Custody Problem: What Passkeys Really Store, and Who Can Take Them Away
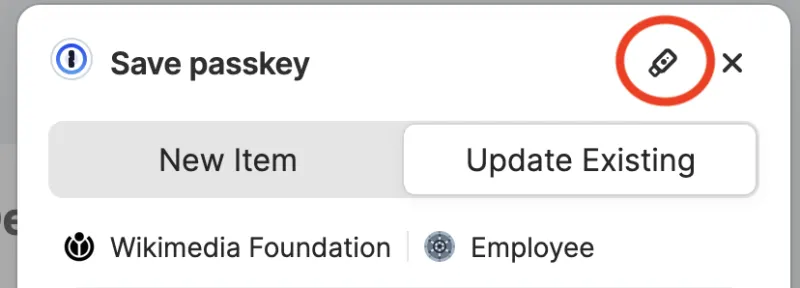
Photo: SLyngshede-WMF, CC BY-SA 4.0, via Wikimedia Commons
The Pitch and the Plumbing
Passkeys are being marketed as the clean end of a messy era. Instead of remembering a password, you unlock your phone with a face or fingerprint, and a website lets you in. In 2026, the pitch has moved from tech conferences into ordinary American banking apps, insurance portals, and retail accounts. The security argument is real: passkeys are built on public-key cryptography, and the private half of the credential is designed never to leave the authenticator that holds it. But the phrase 'passwordless' hides a custody arrangement. To understand what you gain, you first have to see what you hand over.
A passkey is not a single file you can copy from one app to another. It is a credential pair. When you create a passkey, your device or password manager generates a private key and registers the matching public key with the service. During sign-in, the service sends a challenge; the authenticator signs it with the private key; the service verifies the signature with the public key. The private key never crosses the network. That is a meaningful defense against phishing, because a fake site cannot obtain a usable secret just by collecting what you type.
What the Authenticator Actually Holds
The important question is where that private key lives and who controls the recovery path. A device-bound passkey stays in a single hardware authenticator, such as a security key or a phone's secure enclave. It is portable only if you carry the device. A synced passkey is copied, in encrypted form, through a platform account: iCloud Keychain, Google Password Manager, or a similar service. Syncing makes life easier, because a new phone can inherit the credential. It also means the platform account becomes part of your login chain.
Services typically store the public key, a credential identifier, and metadata about the authenticator. Some deployments also use attestation, which can reveal the type of device or platform that created the credential. That information can help a bank assess risk, but it can also become a way to distinguish among users. The passkey itself is not a secret database of your behavior. The surrounding account, however, can become a map of which services you use and which device you use to reach them.
Recovery Is the New Front Door
Password systems have a familiar weak point: the reset email. Passkey systems move that weak point rather than eliminate it. If you lose the device and cannot access the synced platform account, recovery may depend on a backup device, a recovery code, a trusted contact, or a support desk. Each path has its own security properties. A recovery code kept in a drawer can be strong. A support agent persuaded by a caller's personal data can be weak. The user rarely sees which path a service will choose until something goes wrong.
This is why the most useful passkey question is not whether it stops phishing. It usually does. The better question is 'What happens when I lose custody?' A service that allows only one passkey, with no hardware key and no printed recovery code, has created a single point of failure that happens to be convenient. A service that permits several passkeys across devices and platforms gives you room to recover without begging.
Portability and the Convenience Trap
Cross-platform portability is improving, but it is not yet uniform. Standards work on credential exchange has aimed at letting passkeys move between ecosystems, and major platforms have announced support in recent years. In practice, the experience still depends on the service and the manager. Some accounts let you add a passkey from a different platform. Others tie enrollment to a single app or device. The result is a quiet form of lock-in: not a contract that forbids leaving, but a pile of credentials that are easiest to keep where they are.
For US users, the lock-in can appear in small, practical moments. You switch from an iPhone to an Android phone, or from a Mac to a Windows laptop, and discover that a dozen accounts need to be re-enrolled. The websites still work, but the friction is enough to make you delay. That delay is the product. Convenience is not neutral when it shapes which platform you stay on.
A Custody Checklist
The reasonable response is not to reject passkeys. It is to treat them as credentials with a custodian. Add more than one passkey to important accounts, including a hardware security key where the service supports it. Keep recovery codes offline. Know whether a passkey is synced or device-bound. Test the export or transfer path before you depend on it. Ask whether the service lets you delete a passkey and fall back to another method. And remember that the platform account protecting your passkeys deserves the same scrutiny as the accounts the passkeys unlock.
Passkeys can make the web safer and simpler at the same time. They can also concentrate authority in the accounts we already use every day. The difference is custody, and custody is the part the marketing rarely explains.